Social engineering
When someone lies their way in by phone, message or in person, pretending to be a colleague, a funder or tech support.
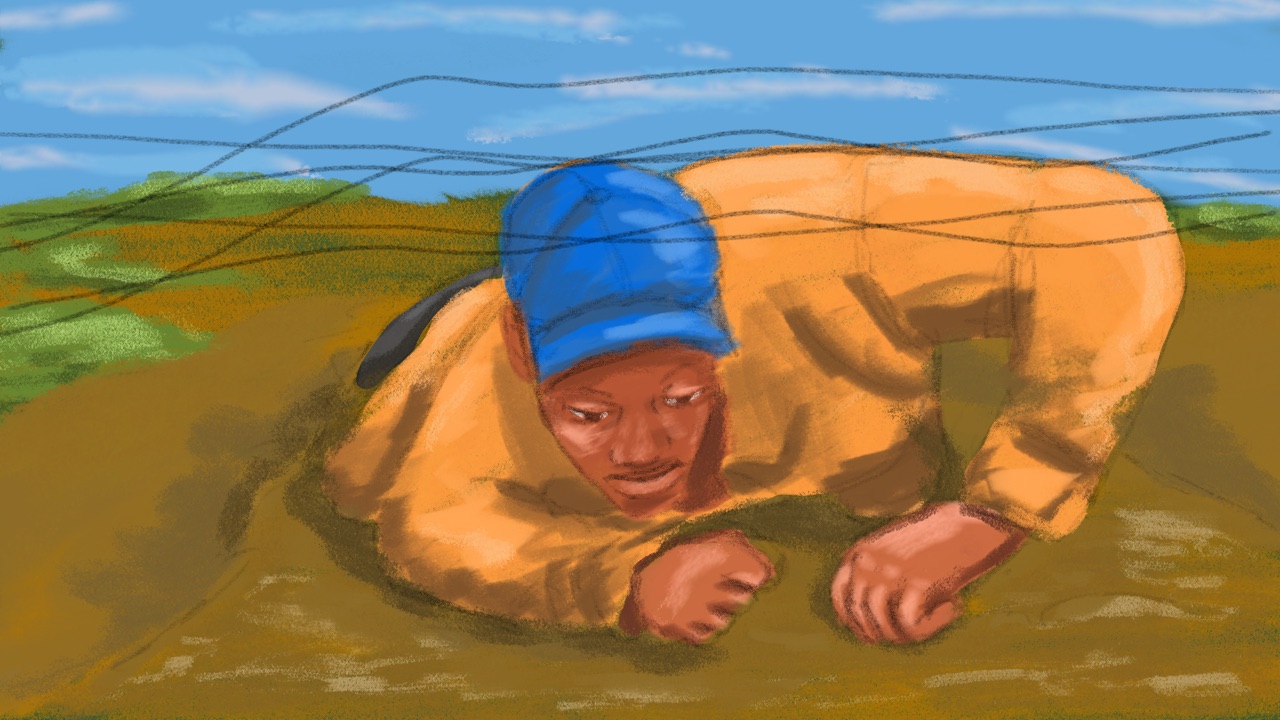
Samuel directs a legal aid organisation in Addis Ababa, Ethiopia, and often talks to the press about his team’s cases. One afternoon a WhatsApp message arrives from a woman who says she’s a reporter at an international news outlet, writing about legal aid across the region. She knows the names of two of his cases, asks for a short interview, then sends a link to “the questions” that asks him to sign in. Something about the link feels off. Samuel finds the outlet’s press office on its own website and calls: nobody there has heard of her.
What it looks like
Social engineering is lying your way in: getting someone to hand over money, a code, information or access with a story, a borrowed name or a sense of urgency (Access Now). It arrives by phone, chat, voice note, email, social media and in person (SIIRF; EFF; Security in a Box). Impersonation, pretending to be a real person or organisation, is one of its main tools (Data Detox Kit; Digital First Aid Kit).
It works on people rather than technology. Even well-funded attackers still need someone to click a link, open a file or install something (Access Now). The careful ones invest: they build a relationship over time and across channels, and borrow the names of real people the target trusts (Access Now; Citizen Lab). Their raw material is what your organisation publishes: names, roles, projects and events from your website and social media (SIIRF), and AI now makes it cheap to tailor a message to one person (Data Detox Kit). Doxxing shows how to see what’s out there.
Why groups like yours are targeted
Small organisations run on trust and quick replies, and they need funding, so a generous offer or an urgent request from a familiar name lands (SIIRF). Two kinds of people try it. Criminals want money. Others want information about your work, your sources or your members: Access Now documented attackers in the Middle East and North Africa spending time and effort to build a connection with journalists through several channels (Access Now), and Citizen Lab found the same impersonated people and fake security alerts reused against diaspora activists and journalists (Citizen Lab).
The stories people tell
- The funder or partner. A grant, award, conference place, paid trip or job you never applied for, followed by a fee, a deposit, bank details or a form (SIIRF). The Ford Foundation says it never asks grantees for deposits or fees to release funding, never asks for bank details and doesn’t approach individuals with grant offers (Ford Foundation). Christian Aid has warned about fake volunteering adverts in Uganda that charged a fee to apply (Christian Aid).
- The colleague or director. A message from a new number saying it’s them, a voice note, a call in a familiar voice, or a real colleague’s hacked account, asking urgently for money, a code or a file (EFF; Data Detox Kit). The voice may be a voice clone: AI software trained on a short clip of someone’s voice can make audio that sounds almost exactly like them (Data Detox Kit). The essay on AI and machine learning security looks at these fakes.
- The journalist, researcher or ally. Interview requests and invitations from people posing as reporters, researchers or supporters, sometimes using a real person’s name (Citizen Lab). The aim is a click, an account or information, and sometimes a meeting. A reporter who received months of fake interview requests told Reporters Without Borders: “Once one of these supposed journalists even suggested that we meet” (RSF).
- The bank, mobile operator or mobile money agent. A caller who knows your name asks you to read out a code or a PIN, or to send back money “sent by mistake” (SIIRF; Data Detox Kit). Someone who knows enough about you can also pose as you to your mobile operator and move your number to their own SIM card, a SIM swap (EFF).
- Tech support or the platform’s security team. A message or call saying your account will be closed, asking you to install an app that lets them control your computer, approve an app, share a code or switch off a security feature, often in an insistent, frightening tone (EFF; Access Now; SIIRF). Fake security alerts are a favourite disguise (Citizen Lab); Spyware and surveillance shows how to check a real one.
- Someone at the door. A delivery, repair or cleaning visit that wanders beyond reception, or a visitor who asks to plug something into your printer or computer (Security in a Box).
- The new member. A volunteer or recruit who joins to record what the group does, or to provoke it into something illegal (Holistic Security).
The signs
- Pressure: urgency, secrecy, fear or flattery, or a request to skip the usual process (SIIRF; EFF; Citizen Lab).
- An unusual ask: a PIN, a code, a password, bank details, a fee, remote access or your approval for an app. Real services don’t ask for codes or passwords (SIIRF; Access Now).
- Something slightly wrong: a new number, a name or address that’s nearly right, such as a double hyphen in an email address, or a channel the person doesn’t usually use (Access Now; Christian Aid).
- A feeling: it seems off.
That last one counts:
In many cases, it helps to trust your instincts: If something feels off or you are being pressured or rushed to take action, take a step back and check in with your peers before moving forward.
Access Now Digital Security Helpline, on a campaign against civil society
Checking another way
Checking another way means confirming a request through a channel you already trust, never the one it arrived on.
- Slow it down. Say you’re in the middle of something and will call back, then end the conversation (Data Detox Kit).
- Contact them a way you already have, or find yourself. A saved number or the official website, never the number, link or address in the message (Access Now). Display names can be copied, and as the Data Detox Kit warns, “Don’t rely on caller ID, as scammers can easily change that to disguise their identity” (Data Detox Kit).
- If you can’t reach them, ask someone you trust. They can check for you (Access Now). For a message from a platform’s “security team”, search whether that service ever contacts users by direct message (Access Now).
- Test a voice you’re not sure of. Ask something only the two of you know, or ask them to message you from another account (EFF).
- Never share a code, PIN or password, whoever asks. Two-factor codes are for typing into the official site, not for reading out to anyone (Access Now).
- Before money moves, follow the payment rule. Any change to bank details or any urgent payment is confirmed by phone, on a number you already have (SIIRF). Phishing has more.
Make it a team rule, written into your security policies: requests for money, codes, files or access get checked another way first, whoever they seem to come from, the director included.
Infiltration, without witch-hunts
Infiltration is a real risk for activist groups, but treating suspected informants as enemies doesn’t help. Holistic Security points out that informants are often victims too, and that an atmosphere of suspicion and mistrust can lead to witch-hunts that harm the group and its cause (Holistic Security). Protect the group instead:
- Agree openly how sensitive information is handled and who sees what, so a newcomer can’t reach much (Holistic Security). Who has access helps you sort it.
- Look again at what really needs to be secret, and what could be open (Holistic Security).
- Keep the group’s activities lawful and non-violent, and treat anyone pushing for illegal or violent methods with caution (Holistic Security).
If it happens
- If you typed a password, shared a code or approved an app, go to Account taken over.
- If you opened a file or clicked a link, go to Clicked a bad link.
- If money or payment details went, call your bank or mobile money provider straight away. Speed matters (SIIRF).
- If someone is posing as your organisation or a colleague, keep screenshots first, then warn your contacts from an account you fully control, and report the fake to the platform (Digital First Aid Kit). Social media accounts covers reporting fake accounts.
- Tell the people who were impersonated, through a contact you already have, so they can warn their own networks (SIIRF).
- Warn the team. The same story often reaches several people at once (SIIRF; Citizen Lab).
Supporting the person
Being conned is embarrassing, and the shame can keep people quiet and make them pull away (Data Detox Kit). These stories are built to work on careful people:
There is no character flaw or single common mistake for those falling prey to scammers, and even experts can get hit.
Safa Ghnaim, Tactical Tech, Data Detox Kit
Thank whoever reports it, even late, and never blame them. A trusted circle, people you can call when a message feels wrong, helps before a scam and after one (Data Detox Kit). Well-being and care has more on a team where people can report mistakes.
Teach it to your team
A session of about 25 minutes. Practise in the open: don’t test colleagues with fake calls or messages, which embarrasses people and can turn them away from security altogether (SAFETAG). Training your team has more on practising without tricks.
- Prepare: three or four stories from this guide, or real ones your team has received, with names removed.
- Exercise: read out Samuel’s afternoon, stopping before the end, and ask what he should do. Then pair up: one person plays “the bank” asking for a code, the other practises ending the call and ringing back on the official number. For more practice, use a quiz such as Shira, which covers fake messages across email, texts, chat apps and social media.
- Three questions: What do you say when a caller asks for a code? How do you check a message from a new number that says it’s the director? Who do you tell when something feels off?
- Afterwards: offer one-to-one time to anyone who has been caught out before, and post new scams in the team chat as they appear.
More in Common Risks
Doxxing
When someone publishes your staff's home addresses, phone numbers or family details to intimidate them, and how to shrink what can be found in the first place.
Online harassment and abuse
Harassment and intimidation campaigns aimed at your staff, including by extremist groups, and how to support the colleagues on the receiving end.
Spyware and surveillance
Recognising when your devices, communications or meetings may be monitored, from spyware to physical surveillance, and the basic counter-measures that help.